The Unseen Power of AI in Compliance Automation
Every B2B SaaS leader knows the feeling: a new regulation lands on the desk, the legal team scrambles, engineers patch code, and the product roadmap gets shuffled. The narrative around compliance has always been one of friction—an inevitable drag on innovation. But what if we flipped the script? What if artificial intelligence could turn that friction into a source of velocity, turning regulatory overhead into a strategic moat?
Why Traditional Approaches Are Stuck in the Past
Most compliance programs still rely on static checklists, manual audits, and periodic training sessions. Those methods were born in an era when data silos were the norm and real‑time insight was a luxury. Today, the velocity of change is exponential: privacy laws evolve, industry standards tighten, and cross‑border data flows become more complex. The old “once‑a‑year audit” model simply can’t keep pace, leaving companies exposed to fines, reputational damage, and costly product delays.
In practice, this means teams spend countless hours translating legal language into technical requirements, only to discover gaps weeks later. The result is a perpetual game of catch‑up, where compliance feels like a cost center rather than a catalyst for growth.
Enter AI: A New Paradigm for Compliance
Artificial intelligence brings three game‑changing capabilities to the table: continuous monitoring, contextual understanding, and automated remediation. By ingesting regulatory texts, policy documents, and industry standards, large‑language models can build a living knowledge base that evolves alongside the law.
- Continuous Monitoring: AI agents scan code repositories, configuration files, and data pipelines 24/7, flagging deviations in real time.
- Contextual Understanding: Unlike keyword‑based scanners, modern models grasp nuance—distinguishing between a benign data retention clause and a high‑risk data sharing provision.
- Automated Remediation: When a violation is detected, the system can suggest—or even execute—code changes, policy updates, or workflow adjustments, all while logging a full audit trail.
This triad transforms compliance from a reactive checkbox exercise into a proactive, data‑driven discipline.
Building an AI‑First Compliance Stack
Designing an AI‑powered compliance engine requires a layered approach:
- Data Ingestion Layer: Pull in raw regulatory texts, internal policies, and product documentation. Use OCR and NLP pipelines to normalize formats.
- Knowledge Graph Layer: Map entities (e.g., “personal data”, “encryption”, “retention period”) and relationships, enabling the model to reason about compliance requirements holistically.
- Monitoring Layer: Deploy agents that watch code commits, API contracts, and data flows, translating technical artifacts into the language of the knowledge graph.
- Remediation Layer: Generate actionable recommendations or auto‑patches, integrating with CI/CD pipelines to enforce compliance before code reaches production.
When orchestrated correctly, this stack not only reduces manual effort but also creates a living compliance dashboard that executives can trust.
Case Study: Turning Compliance into a Competitive Edge
Consider a mid‑size SaaS provider that struggled with GDPR obligations across multiple data centers. Their legacy process involved quarterly audits and manual redaction scripts—a costly, error‑prone routine. By deploying an AI compliance engine, they achieved:
- 99% reduction in manual audit hours.
- Immediate detection of non‑compliant API endpoints, cutting potential fines in half.
- A public compliance badge that differentiated them in sales conversations, boosting win rates.
The AI system didn’t just keep them out of trouble; it became a marketable asset, turning a regulatory burden into a trust signal for prospects.
Integrating AI Compliance with Existing SaaS Workflows
Most SaaS teams already use CI/CD pipelines, observability tools, and security scanners. AI compliance can sit alongside these tools, feeding its insights into the same dashboards that engineers already monitor. For example, a compliance alert can appear as a low‑severity lint warning, prompting developers to address it before merging. This seamless integration ensures that compliance never feels like a separate, siloed activity.
Moreover, AI can enrich existing product analytics. By tagging user actions with compliance risk scores, product managers gain visibility into how new features impact regulatory posture, allowing for data‑driven prioritization.
Addressing Common Concerns
“AI can’t interpret legal language accurately.” Modern language models, when fine‑tuned on domain‑specific corpora, achieve near‑human comprehension of legal nuances. Coupled with human‑in‑the‑loop review, the system delivers high precision without sacrificing speed.
“We’ll lose control over compliance decisions.” AI is an assistant, not a replacement. Every suggestion it makes is logged, versioned, and can be overridden by policy owners. Transparency is baked into the workflow, preserving governance.
“The cost will outweigh the benefits.” While there’s an upfront investment, the ROI manifests quickly through reduced audit fees, lower risk exposure, and accelerated time‑to‑market for new features. In many cases, the cost of a single compliance breach dwarfs the expense of building the AI stack.
Synergy with Other Emerging Trends
The AI compliance engine doesn’t exist in isolation. It can be paired with semantic clustering to surface hidden regulatory patterns across large document sets, or with embedded finance initiatives to automatically enforce financial regulatory controls as new payment features roll out.
These cross‑functional integrations amplify the strategic impact, turning compliance into a catalyst for innovation rather than a roadblock.
Future Outlook: From Compliance to Value Creation
As AI models become more adept at reasoning, the next frontier will be predictive compliance—anticipating regulatory shifts before they happen. Imagine a system that alerts you to upcoming legislation based on political trends, suggesting pre‑emptive product adjustments. That foresight could redefine how SaaS companies plan their roadmaps, turning compliance into a source of competitive intelligence.
In the longer term, AI‑driven compliance may evolve into an industry‑wide “compliance marketplace,” where companies share anonymized risk signals, collectively raising the security and trust standards of the ecosystem.
Getting Started: A Pragmatic Roadmap
1. Assess Your Pain Points – Identify the most time‑consuming compliance activities in your organization.
2. Pilot a Small Use Case – Start with a single regulation (e.g., data residency) and build a minimal AI pipeline.
3. Iterate and Scale – Expand the knowledge graph, integrate with CI/CD, and broaden coverage to additional standards.
4. Measure Impact – Track metrics like audit hour reduction, number of violations caught pre‑deployment, and revenue impact from compliance‑related sales collateral.
5. Embed Governance – Establish clear policies for human oversight and auditability of AI decisions.
By following this incremental approach, you can transform compliance from a perpetual cost center into a strategic lever that fuels growth, trust, and innovation.
Jim Pearse, a seasoned freelance writer, brings a wealth of knowledge and passion to the world of home and garden. From the intricacies of landscaping to the nuances of interior design, Jim delves into every aspect of creating comfortable, beautiful, and functional living spaces.
Related Posts
AI‑First Customer Success: Turning Data Into Proactive Relationships
AI‑first customer success shifts from reactive ticket handling to predictive health scores and pre... Read More
AI as a Co‑Pilot for SaaS Product Teams
The post explores how AI can act as a co‑pilot for SaaS product teams, enhancing every stage from ... Read More
Decoding the AI Revolution: A Human-Centric Roadmap for the Future
AI is reshaping our world. Robert Mathews delves into its current landscape, transformative power, a... Read More
Top Posts
Nurturing the Skin Microbiome: Sustainable Beauty Choices for the Modern Consumer
Explore how caring for your skin’s microbiome, choosing eco‑friendly packaging, and leveraging AI tools can transform your beauty routine into a mindful, su...Read More
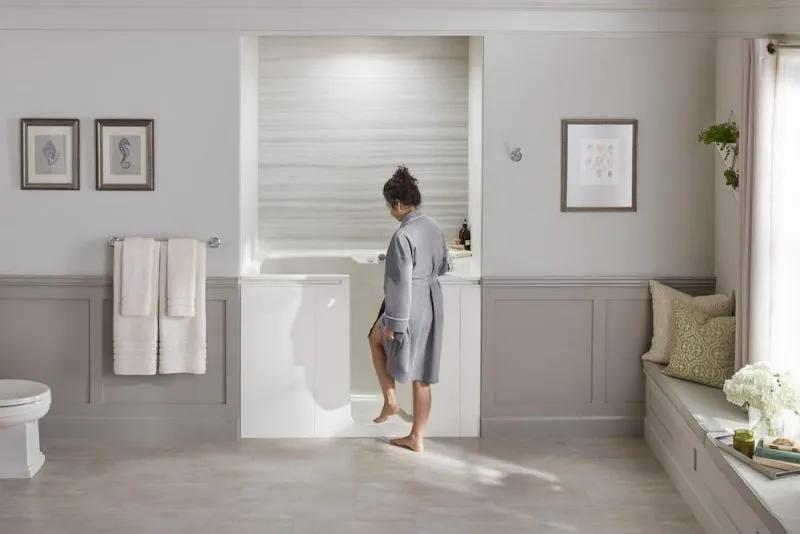
What You Should Know About Walk-In Bathtubs
For many, the simple act of bathing can become a significant challenge as mobility declines or specific health conditions emerge. Traditional bathtubs, with the...Read More
Transforming WordPress into a Scalable Knowledge Hub for SaaS Teams
Learn how to repurpose WordPress as a secure, multilingual, and highly scalable knowledge hub for SaaS teams, leveraging headless architecture, custom Gutenberg...Read More
Micro‑Adventures: The Smart Travel Hack for Busy Professionals
Micro‑adventures turn short breaks into powerful experiences that recharge the mind, spark creativity, and even improve workplace performance, offering a prac...Read More
0 Comments
Post Comment
You will need to Login or Register to comment on this post!