Why Traditional WordPress Security Falls Short
WordPress powers more than a third of the web, making it a magnet for opportunistic attackers. The default security model—relying on strong passwords, occasional updates, and a trusted admin—was never designed for the scale and sophistication of today’s threat landscape. Hackers now blend automated credential‑stuffing bots, supply‑chain compromises, and zero‑day exploits into coordinated campaigns that can bring down an entire site in minutes.
Most site owners treat security as an afterthought: they install a popular plugin, click “activate,” and assume they’re safe. This mindset creates a false sense of security, because the plugin ecosystem itself is a massive attack surface. Vulnerable or malicious plugins, outdated core files, and misconfigured server environments become entry points for attackers.
Enter Zero‑Trust: A Paradigm Shift for WordPress
Zero‑trust is a security philosophy that assumes no component—user, device, or code—is trustworthy by default, even if it resides inside the network perimeter. Applying this mindset to WordPress means every request, every plugin, and every piece of code must prove its legitimacy before being granted access.
Implementing zero‑trust on a WordPress site involves three core principles:
- Never trust, always verify. Every HTTP request is authenticated and authorized, regardless of its origin.
- Least‑privilege access. Users, themes, and plugins receive only the permissions they absolutely need.
- Continuous monitoring. Real‑time telemetry informs security decisions, enabling rapid detection and automated response.
When these principles are baked into the WordPress stack, the platform becomes resilient against both external attacks and insider threats.
Layered Defense: The Five Pillars of a Zero‑Trust WordPress Fortress
1. Harden the Core and Server Environment
Start at the foundation. Move WordPress off shared hosting onto a dedicated environment such as a Virtual Private Server (VPS). While many think of VPS as a cost‑saving measure, they also provide isolation that dramatically reduces blast radius when an attacker gains a foothold.
Read more about why a VPS can be a game‑changer in Why Virtual Private Servers Are the Unsung Heroes of Modern Cloud Strategy.
Beyond isolation, enforce file‑system permissions, disable directory listings, and turn off the PHP file editor. Use a reputable web‑application firewall (WAF) that can block known malicious signatures before they reach WordPress.
2. Adopt a Zero‑Trust Plugin Policy
Plugins are the lifeblood of WordPress but also its Achilles’ heel. Instead of installing anything that promises a quick feature, establish a vetting pipeline:
- Check the plugin’s development history: frequency of updates, number of active installations, and community reviews.
- Scan the code with static analysis tools for known vulnerable functions.
- Run the plugin in a sandbox environment to monitor its behavior before deploying to production.
- Prefer plugins that are signed or distributed via a trusted marketplace with rigorous security audits.
This “trust‑but‑verify” approach mirrors the zero‑trust mindset: every piece of code must earn its place.
3. Enforce Multi‑Factor Authentication and Role‑Based Access
Passwords alone are insufficient. Enforce multi‑factor authentication (MFA) for all admin and editor accounts. Pair MFA with role‑based access control (RBAC) to ensure users can only perform actions aligned with their responsibilities. For example, a content author should never have the capability to install plugins or modify core files.
4. Continuous Runtime Monitoring and Automated Response
Security is no longer a set‑and‑forget activity. Deploy agents that monitor file integrity, login anomalies, and API usage in real time. When an abnormal event—such as a sudden surge of failed login attempts or an unexpected file change—is detected, the system should automatically:
- Isolate the affected component (e.g., switch the site to maintenance mode).
- Notify security personnel via Slack or email.
- Roll back the compromised files from a known‑good backup.
Automation shortens the mean time to detect (MTTD) and mean time to respond (MTTR), which are critical metrics in a zero‑trust environment.
5. Leverage AI‑Driven Threat Intelligence
Modern attackers leverage AI to generate polymorphic malware, making signature‑based detection less effective. In response, security teams can adopt AI‑driven analytics that learn normal traffic patterns and flag deviations. These models can be trained on the unique telemetry of your WordPress site, providing a custom defense layer.
For a deeper dive into how AI can reshape content experiences, see Beyond Keywords: A Semantic SEO Playbook for Voice & AI. The same principles apply to security: context‑aware models outperform generic rule sets.
Implementing Zero‑Trust Without Breaking the Site
Transitioning to a zero‑trust architecture may seem daunting, but a phased approach can minimize disruption:
- Audit the current state. Use tools like WPScan to catalog known vulnerabilities.
- Isolate critical assets. Move the admin dashboard behind a VPN or restrict access by IP.
- Upgrade authentication. Deploy MFA and enforce strong password policies.
- Introduce a WAF. Start with a managed WAF that offers out‑of‑the‑box protection.
- Apply plugin vetting. Freeze new plugin installations until the vetting workflow is established.
- Roll out monitoring. Implement file‑integrity monitoring and log aggregation.
- Iterate with automation. Add automated response playbooks for the most common alerts.
Each step builds upon the previous one, creating a cumulative defense that aligns with zero‑trust principles.
Case Study: A Zero‑Trust Turnaround for a Mid‑Size Agency
One of our clients, a digital agency managing 30 WordPress sites for various brands, suffered a supply‑chain breach when a widely used SEO plugin was compromised. The attacker gained admin access across multiple sites, injecting malicious JavaScript that harvested visitor data.
By applying a zero‑trust framework, the agency achieved the following within three months:
- Reduced the attack surface by deactivating 70% of unused plugins.
- Implemented MFA for all user accounts, eliminating credential‑stuffing success.
- Deployed a WAF with custom rules that blocked the malicious payload before it reached the sites.
- Established a CI/CD pipeline for plugins that included static code analysis and automated sandbox testing.
- Integrated an AI‑driven monitoring tool that detected anomalous outbound traffic, triggering an immediate site lockdown.
The result? Zero successful intrusions for the subsequent six months, a 40% drop in support tickets related to security, and restored client confidence.
Future‑Proofing Your WordPress Site
Zero‑trust is not a one‑time project; it’s an ongoing mindset. As the WordPress ecosystem evolves, so will the threats. Here are three forward‑looking practices to keep your site secure:
- Adopt containerization. Run WordPress inside Docker containers with immutable images. If a container is compromised, replace it with a fresh instance from a trusted image.
- Participate in community bounty programs. Many security researchers reward responsibly disclosed vulnerabilities. Engaging with the community helps you stay ahead of emerging exploits.
- Continuous training. Keep your development and operations teams informed about the latest attack vectors—phishing, credential‑stuffing, and supply‑chain compromises.
By treating security as a shared responsibility across people, processes, and technology, you transform WordPress from a vulnerable CMS into a resilient digital asset.
Key Takeaways
- Traditional WordPress security models are inadequate for modern threats.
- Zero‑trust principles—never trust, always verify, least‑privilege, continuous monitoring—provide a robust framework.
- Hardening the server, vetting plugins, enforcing MFA, automating response, and leveraging AI create a layered defense.
- A phased implementation minimizes disruption while delivering measurable security gains.
- Future‑proof your site with containerization, community engagement, and ongoing training.
WordPress security is a journey, not a destination. By embracing zero‑trust, you empower your organization to stay ahead of attackers, protect user data, and maintain the trust that fuels every successful online experience.
David Moore is a freelance writer specializing in two dynamic and ever-evolving fields: gambling and the tech industry. With a keen eye for detail and a knack for unraveling complex topics, David delivers insightful and engaging content that keeps readers informed and entertained.
Related Posts
From Code to Culture: Building a Security‑First Mindset for Your WordPress Team
A practical guide that shifts WordPress security from a technical checklist to a shared team culture... Read More
Zero‑Trust Security Playbook for WordPress Sites
A comprehensive guide to shifting WordPress security from reactive checklists to a proactive zero‑... Read More
Beyond Plugins: A Holistic Approach to WordPress Security
Explore a multi‑layered WordPress security strategy that extends beyond core updates and plugin ch... Read More
Top Posts
Senior Voices: How Older Adults Are Shaping the Next Cultural Wave
Seniors are stepping into the spotlight, using tech, health tools, and sustainable initiatives to become trendsetters and community leaders, reshaping how we vi...Read More
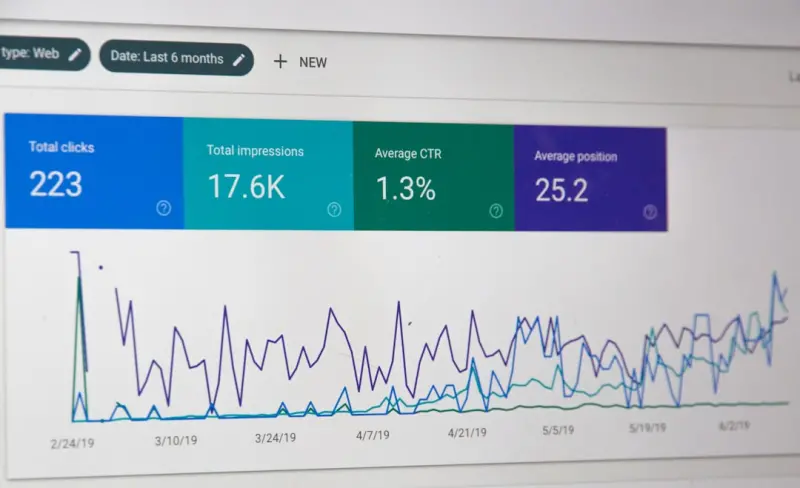
Unlocking Bing’s Hidden Power for B2B SaaS Visibility
Bing isn’t just a backup to Google—its integration with Windows, Edge, and LinkedIn makes it a strategic channel for B2B SaaS. Learn practical steps to opti...Read More
3 Tips To Make Your Daughter's Birthday Special
There are few joys in life quite like witnessing the sheer delight on your daughter's face as she celebrates another year of growth, wonder, and dreams. Her bir...Read More
From Clicks to Conversations: Redefining Google Analytics for B2B SaaS
Turn Google Analytics into a strategic conversation partner by aligning metrics with business goals, fostering a measurement culture, and integrating insights a...Read More
0 Comments
Post Comment
You will need to Login or Register to comment on this post!